
SOC Audit Specialists Strengthening Brand Trust
Seattle-based auditors who understand your tech stack and respect your time.


Our Story

Render Compliance started with a simple frustration.
Beau Butaud, founder, spent years working across three CPA firms – small, medium, and large. The problems were always the same. Audits that dragged on for months. Auditors who didn’t understand the technology they were examining. Clients who dreaded every interaction.
In 2023, he decided to build something different.
The bet was straightforward: deliver high-quality SOC audits fast without cutting corners. Hire auditors who actually know modern tech stacks – cloud infrastructure, SaaS platforms, compliance automation tools. Make the whole process less painful.
Today, we work with B2B SaaS companies and organizations across healthcare, financial services, AdTech, and manufacturing. We serve clients globally from our Seattle headquarters, and we issue reports within three weeks of fieldwork completion.
We’re small by design. You work directly with experienced auditors – not junior staff learning on your dime.
Leadership
Beau Butaud
Information Security Assurance Partner
Beau Butaud, CPA, CISA, MPAcc: Born at a young age near Seattle, WA, Beau will loyally defend the eternally damp weather conditions of the Pacific Northwest. Educated in Business and Accounting at the University of Washington, he began his career in financial statement auditing before pivoting to focus on information security.
He spent a decade in audit, largely in that niche, with a brief stint as a security compliance manager to have a taste of “the other side”, across the audit conference room table.
Always passionate about workflow efficiency and innovative practices, Beau was driven to start Render Compliance in 2023 to build a firm that thrived at the intersection of market-driven quality and efficiency.
When he’s not SOC auditing, you’ll find him spending time with his family, attempting to fix broken things around the house, reading classic fiction, or playing soccer.
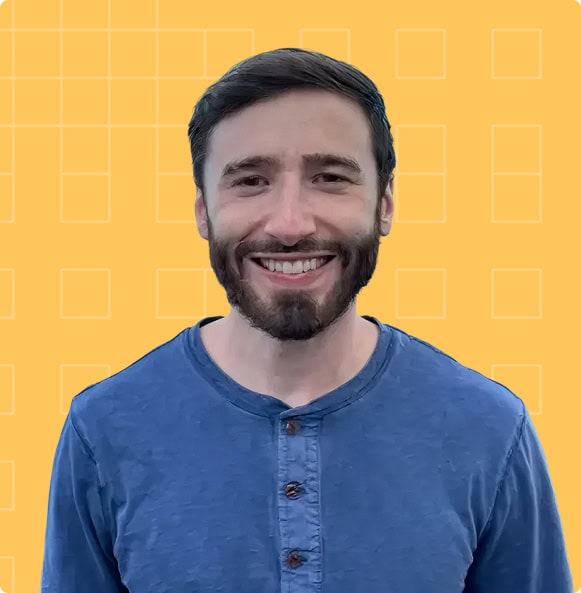
Matthew Corapi
Information Security Assurance Manager
Matt Corapi, CPA, CISA, MBA, and ISO/IEC 27001:2022 Lead Auditor: Born near Syracuse, New York, Matt studied Business Accounting at Niagara University. He did his time in true financial accounting before becoming an IT auditor for the majority of his career.
Matt is always pushing to learn new frameworks, attain new certifications, or understand the inner workings of technologies.
In his free time, Matt takes advantage of everything Bellingham, WA has to offer, as well as traveling around the country. You’ll find him intensely mobile and active, spending time with his wife and friends, with hobbies including running, skiing, foraging, cooking, soccer, and roaming through the woods.
Our Mission
Strengthen brand trust by illuminating data security.
Your prospects want to know their data is safe with you. Your enterprise buyers need proof before they’ll sign. A SOC report isn’t just a compliance checkbox – it’s how you prove you take security seriously.
We exist to make that proof clear, credible, and fast.

Our Values
Audit speak is confusing. We translate it so you actually understand what’s happening and why.
We think critically about what matters for your specific environment. When tools can perform a task better than humans, we use them.
If we don’t know something, we’ll say so. Then we’ll figure it out.
Deadlines slip when no one owns them. We keep projects on track, flag issues early, and yes – we hold ourselves to the same standard.
We’d rather do fewer audits well than scale at the expense of our reputation.
