
Cybersecurity Audits for AI Compliance
Fast audits from a team that’s seen an ML pipeline before.
- Multi-cloud expertise across infrastructure supply chain shared responsibility models
- AI governance controls scoped into your SOC 2 – not bolted on as an afterthought


Most Auditors Don't Audit AI.
We Do.
We help you scope AI-specific controls into your SOC 2 – model versioning, training data access, output validation – so your report actually reflects what you do.
We’ve audited AI-native companies. We help you assess AI Risk Exposure: are you merely exposed to third party AI risk? Are you using AI products internally? Or are you implementing AI into your customer-facing product?
We ensure you’ve properly assessed risk and designed controls to address risks.
We know how to evaluate controls around model accuracy, bias monitoring, and output validation.
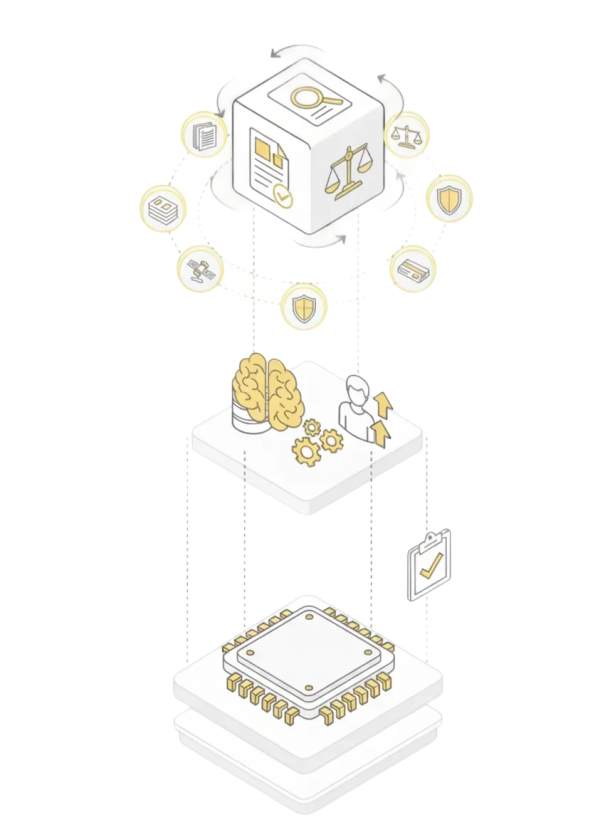
We audit access controls, data lineage, and encryption across your entire ML pipeline – from ingestion to inference.
We’re small by design. Direct access to experienced auditors. No getting lost in large teams and needless chains of approvals.
Services for AI & Cloud Security Companies
Our Latest Articles
We publish educational content to help you understand compliance requirements and prepare for your audit.

Frequently Asked Questions
How do you audit training data access controls?
We review who has access to training datasets, how that access is logged, and what controls exist around data labeling and annotation pipelines. If you’re handling sensitive data in your training sets, we scope controls accordingly.
What about model versioning and change management?
We evaluate your controls around model deployment – version control, approval workflows, rollback capabilities, and how you track which model is in production at any given time.
Do LLM base model provider SOC 2 reports cover our AI Risks?
Possibly, and partially. You should begin by understanding the shared responsibility matrix between your platform, your customers, and your LLM provider. Then assess the third party risks unique to AI implementation over your choice of LLM.
How do you handle multi-cloud environments?
We’ve audited companies running across AWS, Azure, and GCP simultaneously. We scope controls consistently across providers without creating redundant work for your team.
Can you include AI governance controls in our SOC 2?
Yes. We help AI companies address governance around model development, training data handling, and output validation within their SOC 2 scope. Your customers are starting to ask about this – your report should have answers.
What if we're using third-party models or APIs?
We scope controls around how you integrate external AI services – access management, data handling, output validation, and vendor oversight. Your SOC 2 should reflect your actual architecture.